Security
bcrypt passwords, AES-GCM vault, CSRF, SSRF, origin-locked browser, HITL for CAPTCHA/OTP/MFA.
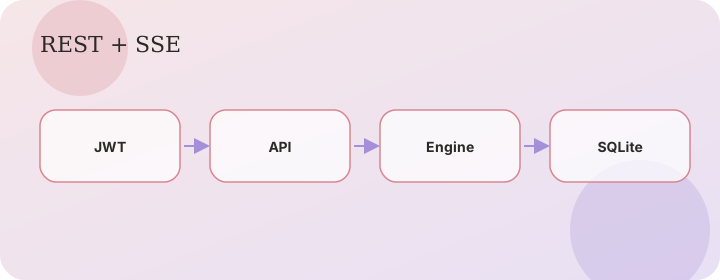
Flow
Passwords
Account passwords are bcrypt (cost 12) with a strength policy and lockout (5 failures / 15 minutes). An optional PASSWORD_PEPPER HMAC is mixed in before bcrypt. Existing unpeppered hashes still verify. Argon2id is a future option for new hashes.
Vault
API keys and site logins are AES-256-GCM. The key is derived with PBKDF2-SHA256 (480k iterations). List endpoints return names only.
Network and browser
JWT is RS256. Mutating requests need CSRF. HTTP tools block private/loopback hosts (SSRF). Browser tools stay on the start site’s registrable domain.
CAPTCHA, OTP, MFA
These are human-only. The workflow pauses (WAITING_APPROVAL). Complete the check in the open browser, then Resume. AgentOS will not fill those fields.
Gmail and .env
Contact SMTP needs a Gmail App Password in CONTACT_SMTP_PASSWORD — never your Google login password. .env is gitignored. On Cloud Run, mount the App Password from Secret Manager.